Subscribe:

Ads 468x60px

Pages

Showing posts with label Linux. Show all posts

Wednesday, June 11, 2014

You (oracle) are not allowed to access to (crontab) because of pam configuration.

You (oracle) are not allowed to access to (crontab) because of pam configuration.

1. Check the cron process/service is running or not
# ps -ef | grep cron
root     10441     1  0 Apr16 ?        00:00:00 crond
root     17805 17148  0 13:00 pts/0    00:00:00 grep cron

# /etc/init.d/crond status
crond (pid  10441) is running...

2. Check the crontab for oracle user
# crontab -l -u oracle

Authentication token is no longer valid; new one required
You (oracle) are not allowed to access to (crontab) because of pam configuration.

Getting above error. check for logs
# less /var/log/cron
Jun 11 11:40:01 linuxtutor1 crond[20496]: (root) CMD (/usr/lib64/sa/sa1 1 1)
Jun 11 11:50:01 linuxtutor1 crond[31752]: (root) CMD (/usr/lib64/sa/sa1 1 1)
Jun 11 12:00:01 linuxtutor1 crond[11037]: Authentication token is no longer valid; new one required
Jun 11 12:00:01 linuxtutor1 crond[11037]: CRON (oracle) ERROR: failed to open PAM security session: Success
Jun 11 12:00:01 linuxtutor1 crond[11037]: CRON (oracle) ERROR: cannot set security context

# less /var/log/secure
Jun 11 13:02:04 linuxtutor1 crontab: pam_unix(crond:account): expired password for user oracle (password aged)
Jun 11 13:03:40 linuxtutor1 su: pam_unix(su-l:session): session opened for user oracle by root(uid=0)
Jun 11 13:03:49 linuxtutor1 crontab: pam_unix(crond:account): expired password for user oracle (password aged)
Jun 11 13:05:14 linuxtutor1 su: pam_unix(su-l:session): session closed for user oracle
Jun 11 13:11:46 linuxtutor1 chage[30384]: changed password expiry for oracle

User oracle account is expired on 10th june 2013
# chage -l oracle
Last password change                                    : May 13, 2013
Password expires                                        : Jun 10, 2014
Password inactive                                       : never
Account expires                                         : never
Minimum number of days between password change          : 7
Maximum number of days between password change          : 28
Number of days of warning before password expires       : 7

# date
Wed Jun 11 13:10:28 EDT 2013

Change oracle user's password to never expire
# chage -M 99999 -m 99999 oracle

Check the user's password age
# chage -l oracle
Last password change                                    : May 13, 2013
Password expires                                        : never
Password inactive                                       : never
Account expires                                         : never
Minimum number of days between password change          : 99999
Maximum number of days between password change          : 99999
Number of days of warning before password expires       : 7

Check the oracle user's crontab entries. Now it is displaying the cron details.
# crontab -l -u oracle
0 * * * * /home/oracle/bin/check-db-status

Now the cron jobs are running fine without any issues.
Read more...

Thursday, April 4, 2013

Autologin through SSH using bash script

Autologin using bash script

1. Create a new ssh RSA keygen:
[root@linuxtutors# ~]# ssh-keygen -t rsa
Generating public/private rsa key pair.
Enter file in which to save the key (//.ssh/id_rsa):
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in //.ssh/id_rsa.
Your public key has been saved in //.ssh/id_rsa.pub.
The key fingerprint is:
4a:0d:db:6a:06:c9:c8:62:e0:f3:cb:93:5f:de:d6:f4 root@-i

Keys are stored at /.ssh/ directory:
[root@linuxtutors# ~]# cd /.ssh/

List the files
[root@linuxtutors# .ssh]# ls -l; cd
total 6
-rw-------   1 root     root         883 Apr  4 17:50 id_rsa
-rw-r--r--   1 root     root         217 Apr  4 17:50 id_rsa.pub
-rw-r--r--   1 root     root         633 Apr  4 17:43 known_hosts

2. Create the Bash Script to copy public key to remote server:
[root@linuxtutors# ~]# vi autossh.sh
#!/bin/bash
ips=/tmp/List_Of_Machine_IPs.txt
for x  in $(cat $ips)
do

cat .ssh/id_rsa.pub | ssh root@$x 'cat >> .ssh/authorized_keys'
cat .ssh/id_rsa.pub | ssh root@$x 'cat >> .ssh/authorized_keys2'
ssh root@$x 'chmod 640 .ssh/authorized_keys'
ssh root@$x 'chmod 640 .ssh/authorized_keys2'
ssh root@$x 'chmod 700 .ssh'
done

Save and Exit:
:wq

3. Assign the execute permission to the script:
[root@linuxtutors# ~]# chmod a+x autossh.sh

4. List all the machine ip which you want to autologin:
[root@linuxtutors# ~]# vi /tmp/List_Of_Machine_IPs.txt
192.168.1.100
192.168.1.101
192.168.1.102

Save and Exit:
:wq

5. Execute the script
[root@linuxtutors# ~]# sh autossh.sh
The authenticity of host '192.168.1.100 (192.168.1.100)' can't be established.
RSA key fingerprint is ae:14:11:0f:cc:2a:28:03:b4:13:7f:35:ce:ab:f5:ee.
Are you sure you want to continue connecting (yes/no)? yes
Warning: Permanently added '192.168.1.100' (RSA) to the list of known hosts.
root@192.168.1.100's password:
The authenticity of host '192.168.1.101 (192.168.1.101)' can't be established.
RSA key fingerprint is ae:14:11:0f:cc:2a:28:03:b4:13:7f:35:ce:ab:f5:ee.
Are you sure you want to continue connecting (yes/no)? yes
Warning: Permanently added '192.168.1.101' (RSA) to the list of known hosts.
root@192.168.1.101's password:
The authenticity of host '192.168.1.102 (192.168.1.102)' can't be established.
RSA key fingerprint is ae:14:11:0f:cc:2a:28:03:b4:13:7f:35:ce:ab:f5:ee.
Are you sure you want to continue connecting (yes/no)? yes
Warning: Permanently added '192.168.1.102' (RSA) to the list of known hosts.
root@192.168.1.102's password:
[root@linuxtutors# ~]# 

Read more...

Sunday, March 3, 2013

Passed RHCE

Hey guys, i returned to my blog after a long time. Now i have passed the RHCE exam on RHEL 6.0 with a score of 100% in RHCSA and 91% in RHCE

            Lot of thanks to all for following my blogs.


Read more...

Wednesday, September 7, 2011

EX442 System Monitoring and Performance Tuning Certificate of Expertise


Systems Monitoring and Performance Tuning

EX442 System Monitoring and Performance Tuning Certificate of Expertise
  • use utilities such as vmstat,iostat,mpstat,sar, gnome-system-monitor, top and others to analyze and report system behavior
  • configure systems to provide performance metrics over a network via SNMP
  • query system performance metrics using SNMP
  • configure graphical SNMP client utilities such as MRTG,RRDtool, etc.
  • use the Pluggable Authentication Modules (PAM) mechanism to implement restrictions on critical system resources
  • use /proc/sys, sysctl and /sys to examine and modify and set kernel run-time parameters
  • use utilities such as dmesg, dmidecode, x86info, sysreport etc. to profile system hardware configurations
  • analyze system and application behavior using tools such as ps, strace, top, OProfile and Valgrind
  • configure systems to run SystemTap scripts
  • alter process priorities of both new and existing processes
  • configure systems to support alternate page sizes for applications that use large amounts of memory
  • given multiple versions of applications that perform the same or similar tasks, choose which version of the application to run on a system based on its observed performance characteristics
  • configure disk subsystems for optimal performance using mechanisms such as software RAID, swap partition placement, I/O scheduling algorithm selection, file system layout and others
  • configure kernel behavior by altering module parameters
  • calculate network buffer sizes based on known quantities such as bandwidth and round-trip time and set system buffer sizes based on those calculations
Read more...

Tuesday, August 16, 2011

vmstat


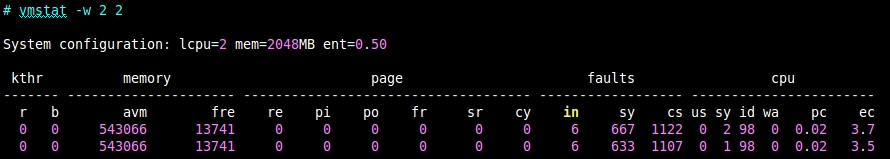
performance issues? first stop vmstat. vmstat is a very useful tool because allows you to have a quick overall performance view of your system and is available in all Unix type systems here some quick a dirty explanations on how to understand the output of the vmstat command... btw I am working on AIX and we will focus on a simple output    1. r should never be smaller than b or we may have a CPU bottleneck due processes suspended due to memory load control 2. if fre is really small and if any paging is going on pi or po this is most likely a cause of a bottleneck  3. if b and wa are high we may have an I/O bootleneck due the number of blocking processes 4. if b is low or normal and free is small and us + sy = (close to 100) then we have a memory bottleneck 5. if us+sy average more than 80% we may have a CPU bootleneck if you are at 100 our system is breathing heavily 6. if us+sy is small but wa is greather than 25 we may have I/O intensive activitie or disk subsystem might not be balanced properly which turns on cpu not being able to work as hard as he can 7. if us+sy is over 80% and r is larger than [5 * (Number of processors - Number of bound processors)] then we have a CPU bound 8. if r is greater than the number of CPUs, there is at least one thread waiting for a CPU and this is likelihood of a performance impact. 9. if sy raises over 10000 per second per processor we may be polling subroutines likes select() indicates a bad code it is advisable to have a baseline measurement that gives a count for a normal sy value.

performance issues? first stop vmstat.

vmstat is a very useful tool because allows you to have a quick overall performance view of your system and is available in all Unix type systems
here some quick a dirty explanations on how to understand the output of the vmstat command... btw I am working on AIX and we will focus on a simple output


1. r should never be smaller than b or we may have a CPU bottleneck due processes suspended due to memory load control
2. if fre is really small and if any paging is going on pi or po this is most likely a cause of a bottleneck
3. if b and wa are high we may have an I/O bootleneck due the number of blocking processes
4. if b is low or normal and free is small and us + sy = (close to 100) then we have a memory bottleneck
5. if us+sy average more than 80% we may have a CPU bootleneck if you are at 100 our system is breathing heavily
6. if us+sy is small but wa is greather than 25 we may have I/O intensive activitie or disk subsystem might not be balanced properly which turns on cpu not being able to work as hard as he can
7. if us+sy is over 80% and r is larger than [5 * (Number of processors - Number of bound processors)] then we have a CPU bound
8. if r is greater than the number of CPUs, there is at least one thread waiting for a CPU and this is likelihood of a performance impact.
9. if sy raises over 10000 per second per processor we may be polling subroutines likes select() indicates a bad code it is advisable to have a baseline measurement that gives a count for a normal sy value.

http://aixperts.blogspot.com/2011/01/performance-issues-first-stop-vmstat.html
From: 
Read more...

vmstat command on Solaris-based Videos

The videos that follow are for vmstat(1M) on Solaris-based operating systems, including Joyent’sSmartOS. All are available here: vmstat videos, and embedded below:


Read more...

touch command

How to change creation date and creation time of existing file

Example:

$ ls -l abc
-rw-rw-r-- 1 sunshine se 16645 Apr 30 10:34 abc
$ touch -t 201003010800 abc
$ ls -l abc
-rw-rw-r-- 1 sunshine se 16645 Mar 1 08:00 abc
==============================================
Option
-t time
Uses the specified time instead of the current time.
time will be a decimal number of the form:

[[CC]YY]MMDDhhmm[.SS]
Read more...

Thursday, August 11, 2011

Zimbra backup


Login as Zimbra
# su – zimbra


stop the zmcontrol service
# service zmcontrol stop


Logout from zimbra
#exit


login as root
# su -


kill all zimbra process
# ps aux | grep zimbra 
# kill -9 pid


Create a directory zcsbackuprsync
# mkdir /zcsbackuprsync


Take a backup of zimbra using rsync
# rsync -avHK /opt/zimbra/ /zcsbackuprsync/zimbra


Create a directory zcsbackuptars
# mkdir /zcsbackuptars


Make tar archive and zip the file
# tar -zcvf /zcsbackuptars/backup.zimbra.version.date.time.tar.gz -C /zcsbackup/zimbra

Read more...

Monday, August 8, 2011

Reinstalling the GRUB Boot Loader


Steps to reinstall a corrupted or mistakenly deleted grub (for RedHat and CentOS systems only) using the rescue mode ::

1.        Boot the system from any boot installation medium like a RedHad #1 CD-ROM or a Flash Drive, etc.

2.      Use the linux rescue command as shown below at the installation prompt to enter the rescue environment:
 linux rescue

3.       Type the command below to mount the root partition:
# chroot /mnt/sysimage

4.      Type the command below to reinstall the GRUB boot loader, where /dev/hda is the boot partition.
# /sbin/grub-install /dev/had
Note: /dev/hda is the boot partition

5.      Go through the /boot/grub/grub.conf file once again, as additional entries may be needed for GRUB so as to make any custom changes there (like controlling another installed operating system).

6.      Finally, reboot the system
Read more...

Difference between .bash_profile, .bash_logout and .bashrc

Important Notes on bash file
  1. These files in your home directories have special meaning to bash, providing a way to setup the account environment when you log in and when you invoke another bash command
  2. If the files are not found in your home directory, you are using the default system on /etc/profile
  3. Most important is the .bash_profile which is read and the command in it is executed by bash every time you logged on to the system.
  4. .bashrc is invoked when you start a new shell or by typing bash on the command line.
  5. If you just need to have the same command run regardless of  a subshell or a login shell, you can easily source .bashrc and hence execute .bashrc from within .bash_profile
  6. .bash_logout is read and executed every time a login shell exits.
Read more...

Installing Linux Kernal-Based Virtual Machine (KVM) on CentOS 5.4 Server

Read more...

Tuesday, August 2, 2011

20 Linux Server Hardening Security Tips Securing your Lin20 Linux Server Hardening Security Tips


Securing your Linux server is important to protect your data,  intellectual property, and time, from the hands of crackers (hackers). The system administrator is responsible for security Linux box. In this first part of a Linux server security series, I will provide 20 hardening tips for default installation of Linux system. 

1: Encrypt Data Communication
2: Minimize Software to Minimize Vulnerability
3: One Network Service Per System or VM Instance
4: Keep Linux Kernel and Software Up to Date
5: Use Linux Security Extensions
6: User Accounts and Strong Password Policy
7: Disable root Login
8: Physical Server Security
9: Disable Unwanted Services
10: Delete X Windows
11: Configure Iptables and TCPWrappers
12: Linux Kernel /etc/sysctl.conf Hardening
13: Separate Disk Partitions
14: Turn Off IPv6
15: Disable Unwanted SUID and SGID Binaries
16: Use A Centralized Authentication Service
17: Logging and Auditing
18: Secure OpenSSH Server
19: Install And Use Intrusion Detection System
20: Protecting Files, Directories and Email
Read more...

Saturday, July 16, 2011

Automatic installation using kickstart method

Question: Let us imagine a scenario where you have to set-up 40 computers on a small company?


Solution:
Even with the network installation method the process is terrible slow . Fortunately for us there is an alternative  ” hands-free” installation method ( non-interactive)  through a featured called kickstart.

The kickstart installation method is used primarily by Red Hat based distributions  to automatically perform unattended operating system installations .The configurations are taken from a file (anaconda.config.cfg)  , so there is no need to be provided  interactively from the user.

Read more...

Thursday, July 7, 2011

Advantages of RHEL6 over RHEL5

Red Hat Enterprise Linux 6 (RHEL6)
RHEL 6

Red Hat Enterprise Linux (RHEL) is an open sourcelinux based operating system developed by Red Hat Inc. It is popularly used as server operating system. Its first release was the RHEl 2.1 which was released in the year 2002. After the first version of RHEL, new and better versions quickly followed like RHEL 3,4,5,etc. Now in 2010, the newest version has been released. It is RHEL 6. Now in this post lets discuss the mainadvantages of RHEL6 over RHEL5


    RHEL6 being the latest release obviously have a lot of new features. The advantages are:
    ·       A new level of virtualization       RHEL6 introduces the use of KVM (Kernel-based Virtual Machine) as its hypervisor. In the earlier releases Xen hypervisor was used. The main advantage of KVM is that a new kernel should not be installed like in Xen. It also supports the installation of many virtual operating systems like Windows, Linux, Solaris,etc. It is easy to manage. 
    ·      Ext4 is made the default filesystem       Ext4 has many new advantages than Ext3 which is used in earlier versions of RHEL. Ext4 is comparatively faster and easy to manage. It supports supports up to 100TB with the addition of Scalable Filesystem Add-one.      
    ·      Improved level of Security       RHEL6 has advanced level of security. SELinux (Security Enhanced Linux) features are improved and a new set of SELinux rules has been added to provide security to virtual machines from hackers and attackers. This new feature is called SVirt. 
    ·       New Networking Features      RHEL6 is released with improved and new networking features. It supportsIPv6. It uses NFSv4 (Network File Transfer) for the sharing of files in the network rather than NFSv3. It also supports iSCSI (internet Small Computer System Interface) partitions. The network manager in RHEL6 supports Wi-Ficapabilities.
    ·       Use of Drivers      RHEL6 has drivers for speeding up operations under KVM, VMware and Xen.
    ·   Increase in the support period provided by Red Hat.       RHEL6 has a long period of support provided by Redhat. It provides updates for 7 years and also a extra 3 years of service as  paid service. Therefore it means that its period of support is twice the period of support provided by other linux distributors like Ubuntu , Debian, etc. 
    ·     Improvements of minor updates       Red Hat releases minor versions such as 6.1, 6.2. These minor versions are the accumulated updates of the major version. The new minor releases will not only contain bug fixes but will also have major changes and new features.    ·       Additional features such as    Your productivity, security and flexibility are enhanced with
    • OpenOffice 3 suite
    • Email - (openchange MAPI client capability)
    • NetworkManager - mobile network connection management
    • Cisco IPSEC client compatibility
    • Smart Card support
    • Encrypted disk (luks)
    • Ext4 file system is introduced.
    • Xen is removed and kernel virtualization machine (KVM) is introduced.
    • Neat command is removed
    • Portmap service is removed.
    • Iscsi is introduced, which supports for SAN.
    • Rpmbuild is available, which is used to create our own rpms.
    • File encyption is added.
    • Palimpsest is available for disk management.
    • Virtual machine will run only on 64bit processors.
    • postfix service is recommended instead of sendmail service.


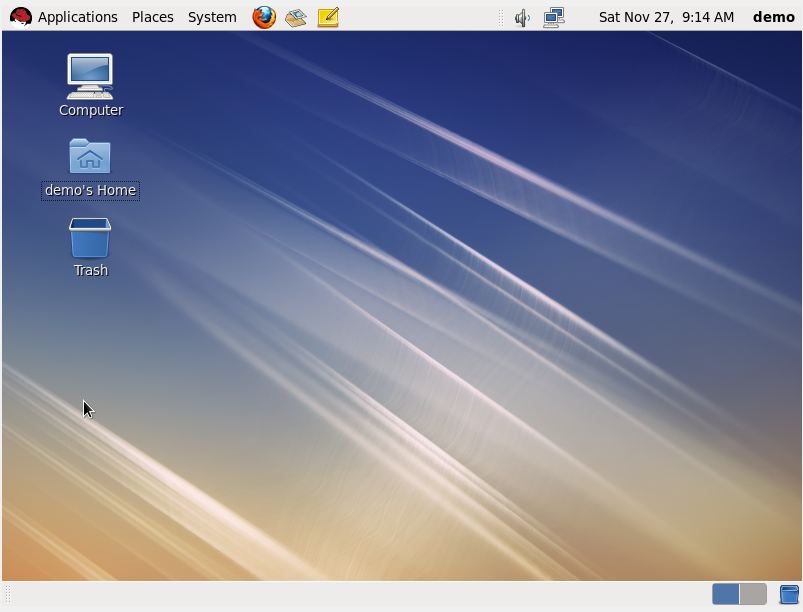
    RHEL6-gnome-desktopRHEL6 has been released with many new feature which make RHEL6 more useful than RHEL5. RHEL6 is somewhat similar to Fedora 12, so the Fedora users should find RHEL6 familiar. Due to all these reasons the release of RHEL6 is a huge step of advancement and also an achievement in the field of open source
       
    Please feel free to comment to make it more useful to everyone.
    Read more...

    Wednesday, May 25, 2011

    Allow a user to "sudo" to root


    Steps require to implement the sudo user:

    1) Run the /usr/sbin/visudo command. 
    # /usr/sbin/visudo

    2) Add the username like this: james ALL=(root) ALL 
    # james ALL=(root) ALL

    3) Save the file and exit from root. Now user “james” should be able to login.
    Read more...

    Tuesday, May 24, 2011

    Linux Interview Questions with Answers


    Q: - What is the difference between ext2 and ext3 file systems?
    The ext3 file system is an enhanced version of the ext2 file system.
    The most important difference between Ext2 and Ext3 is that Ext3 supports journaling.
    After an unexpected power failure or system crash (also called an unclean system shutdown), each mounted ext2 file system on the machine must be checked for consistency by the e2fsck program. This is a time-consuming process and during this time, any data on the volumes is unreachable.
    The journaling provided by the ext3 file system means that this sort of file system check is no longer necessary after an unclean system shutdown. The only time a consistency check occurs using ext3 is in certain rare hardware failure cases, such as hard drive failures. The time to recover an ext3 file system after an unclean system shutdown does not depend on the size of the file system or the number of files; rather, it depends on the size of the journal used to maintain consistency. The default journal size takes about a second to recover, depending on the speed of the hardware.

    Q: - Any idea about ext4 file system?
    The ext4 or fourth extended filesystem is a journaling file system developed as the successor to ext3. Ext4 filesystem released as a functionally complete and stable filesystem in Linux with kernel version 2.6.28.
    Features of ext4 file system:-
    1. Currently, Ext3 supports 16 TB of maximum file system size and 2 TB of maximum file size. Ext4 have 1 EB of maximum file system size and 16 TB of maximum file size.
    [An EB or exabyte is 1018 bytes or 1,048,576 TB]
    2. Fast fsck check than ext3
    3 In Ext4 the journaling feature can be disabled, which provides a small performance improvement.
    4. Online defragmentation.
    5. Delayed allocation
    Ext4 uses a filesystem performance technique called allocate-on-flush, also known as delayed allocation. It consists of delaying block allocation until the data is going to be written to the disk, unlike some other file systems, which may allocate the necessary blocks before that step.

    Q: - How we create ext3 file system on /dev/sda7 disk?
    # mkfs –j /dev/sda7

    Q: - Can we convert ext2 filesystem to ext3 file system?
    Yes, we can convert ext2 to ext3 file system by tune2fs command.
                    tune2fs –j   /dev/<Block-Device-Name>

    Q: - Is there any data lose during conversion of ext2 filesystem to ext3 filesystem? 
    No

    Q: - How we will create ext4 file system?
    # mke2fs -t ext4 /dev/DEV

    Q: - Explain /proc filesystem?
    /proc is a virtual filesystem that provides detailed information about Linux kernel, hardware’s and running processes. Files under /proc directory named as Virtual files. Because /proc contains virtual files that’s why it is called virtual file system.
    These virtual files have unique qualities. Most of them are listed as zero bytes in size. Virtual files such as /proc/interrupts, /proc/meminfo, /proc/mounts, and /proc/partitions provide an up-to-the-moment glimpse of the system's hardware. Others, like the /proc/filesystems file and the /proc/sys/ directory provide system configuration information and interfaces.
    Q: - Can we change files parameters placed under /proc directory? 
    Yes
    To change the value of a virtual file, use the echo command and a greater than symbol (>) to redirect the new value to the file. For example, to change the hostname on the fly, type: 
    echo www.nextstep4it.com > /proc/sys/kernel/hostname 

    Q: - What is the use of sysctl command?
    The /sbin/sysctl command is used to view, set, and automate kernel settings in the /proc/sys/ directory.

    Q: - /proc/ directory contains a number of directories with numerical names. What is that?
    These directories are called process directories, as they are named after a program's process ID and contain information specific to that process.

    Q: - What is RAID?
    RAID, stands for Redundant Array of Inexpensive Disks. RAID is a method by which same data or information is spread across several disks, using techniques such as disk striping (RAID Level 0), disk mirroring (RAID Level 1), and disk striping with parity (RAID Level 5) to achieve redundancy, lower latency, increased bandwidth, and maximized ability to recover from hard disk crashes.

    Q: - Why should we use RAID?
    System Administrators and others who manage large amounts of data would benefit from using RAID technology.
    Following are the reasons to use RAID
    -   Enhances speed
    -   Increases storage capacity using a single virtual disk 
    -   Minimizes disk failure

    Q: - What is the difference between hardware RAID and Software RAID?
    The hardware-based RAID is independent from the host. A Hardware RAID device connects to the SCSI controller and presents the RAID arrays as a single SCSI drive. An external RAID system moves all RAID handling "intelligence" into a controller located in the external disk subsystem. The whole subsystem is connected to the host via a normal SCSI controller and appears to the host as a single disk.
    Software RAID is implemented under OS Kernel level. The Linux kernel contains an MD driver that allows the RAID solution to be completely hardware independent. The performance of a software-based array depends on the server CPU performance and load.

    Q: - What are the commonly used RAID types?
    a. RAID 0            b. RAID 1            c. RAID 5

    Q: - Explain RAID 0?
    RAID level 0 works on “striping” technique. In RAID 0 the array is broken down into strips and data is written into strips. RAID 0 allows high I/O performance but provides no redundancy. RAID 0 Array Size is equal to sum of disks in array. If one drive fails then all data in the array is lost.

    Q: - Explain RAID 1?
    RAID Level 1 is based on Mirroring technique. Level 1 provides redundancy by writing identical data to each member disk of the array. The storage capacity of the level 1 array is equal to the capacity of one of the mirrored hard disks in a Hardware RAID or one of the mirrored partitions in a Software RAID. RAID 1 provides redundancy means good protection against disk failure. In RAID 1 write speed is slow but read speed is good.

    Q: - Explain RAID 5?
    RAID Level 5 is based on rotating parity with striping technique. RAID-5 stores parity information but not redundant data (but parity information can be used to reconstruct data). The storage capacity of Software RAID level 5 is equal to the capacity of the member partitions, minus the size of one of the partitions if they are of equal size. The performance of RAID 5 is based on parity calculation process but with modern CPUs that usually is not a very big problem. In RAID 5 read and write speeds are good.

    Q: - Which kernel module is required for Software RAID?
    “md” module

    Q: - which utility or command is used for creating software RAID’s for RHEL5?
    mdadm

    Q: - Can we create software RAID during Linux installation?
    Yes, we can create Software RAID during Linux Installation by “Disk Druid”

    Q: - What is the role of chunk size for software RAID?
    Chunk size is very important parameter on which RAID performance based.
    We know stripes go across disk drives. But how big are the pieces of the stripe on each disk? The pieces a stripe is broken into are called chunks.To get good performance you must have a reasonable chunk size.
    For big I/Os we required small chunks and for small I/Os we required big chunks.

    Q: - What is SWAP Space?
    Swap space in Linux is used when the amount of physical memory (RAM) is full. If the system needs more memory resources and the RAM is full, inactive pages in memory are moved to the swap space. While swap space can help machines with a small amount of RAM, it should not be considered a replacement for more RAM. Swap space is located on hard drives, which have a slower access time than physical memory.

    Q: - What are the steps to create SWAP files or Partition?
    - Create swap partition or file
    - Write special signature using “mkswap
    - Activate swap space by “swapon –a” command
    - Add swap entry into /etc/fstab file

    Q: - How you will create swap file of size 4 GB and explain swap file entry in /etc/fstab file?
    Use “dd” command to create swap file.
    dd if=/dev/zero  of=/SWAPFILE  bs=1024  count=4
    mkswap /SWAPFILE
    swapon –a
    Entry into /etc/fstab file.
    /SWAPFILE   swap   swap   defaults   0   0

    Q: - Tell me the steps to remove the swap file?
    Firstly disable the swap file by “swapoff” command.
    Remove Swap file entry from /etc/fstab file.
    Now remove the swap file by “rm” command.

    Q: - What can we do with “parted” command or utility?
    - View the existing partition table
    - Add partitions from free space or additional hard drives
    - Change the size of existing partitions

    Q: - How we will check free space on drive /dev/sda with parted command?
    #parted /dev/sda
    Print

    Q: - What is LVM?
    LVM stands for Logical Volume Manager. LVM, is a storage management solution that allows administrators to divide hard drive space into physical volumes (PV), which can then be combined into logical volume groups (VG), which are then divided into logical volumes (LV) on which the filesystem and mount point are created.

    Q: - What are the steps to create LVM?
    - Create physical volumes by “pvcreate” command
    #pvcreate /dev/sda2
    - Add physical volume to volume group by “vgcreate” command
    #vgcreate VLG0 /dev/sda2
    - Create logical volume from volume group by “lvcreate” command.
    #lvcreate -L 1G -n LVM1 VLG0
    Now create file system on /dev/sda2 partition by “mke2fs” command.
    #mke2fs -j /dev/VLG0/LVM1 

    Q: - What is the difference between LVM and RAID?
    RAID provides redundancy but LVM doesn’t provide Redundancy.

    Q: - What are LVM1 and LVM2?
    LVM1 and LVM2 are the versions of LVM. 
    LVM2 uses device mapper driver contained in 2.6 kernel version.
    LVM 1 was included in the 2.4 series kernels.

    Q: - What is Volume group (VG)?
    The Volume Group is the highest level abstraction used within the LVM. It gathers together a collection of Logical Volumes and Physical Volumes into one administrative unit.

    Q: - What is physical extent (PE)?
    Each physical volume is divided chunks of data, known as physical extents; these extents have the same size as the logical extents for the volume group.

    Q: - What is logical extent (LE)?
    Each logical volume is split into chunks of data, known as logical extents. The extent size is the same for all logical volumes in the volume group.

    Q: - How you will check on Your server or system device-mapper is installed or not?
    Check the following file.
    #cat /proc/misc
    if this file contains "device-mapper" term it means device mapper is installed on your system.

    Q: - What is the maximum size of a single LV?
    For 2.4 based kernels, the maximum LV size is 2TB. 
    For 32-bit CPUs on 2.6 kernels, the maximum LV size is 16TB.
    For 64-bit CPUs on 2.6 kernels, the maximum LV size is 8EB.

    Q: - If a volume group named as VG0 already exists but i need to extend this volume group up to 4GB.Explain all steps?
    Firstly create Physical volume (/dev/sda7) of size 4GB.
    Now run following command.
    vgextend VG0 /dev/sda7

    Q: - If a volume group VG0 have 3 PV's (/dev/sda6, /dev/sda7, /dev/sda8) but i want to remove /dev/sda7 pv from this VG0?
    vgreduce VG0 /dev/sda7

    Q: - Which command is used to extend a logical volume?
    lvextend --size +<addsize> /dev/<vgname>/<lvname>
    resize2fs /dev/<vgname>/<lvname>

    Q: - Tell me all steps to remove a LVM?
    To remove a logical volume from a volume group, first unmount it with the umount command:
    umount /dev/<vgname>/<lvname>
    and then use the lvremove command:
    lvremove /dev/<vgname>/<lvname>

    Q: - Is there any relation between modprobe.conf file and network devices?
    Yes, This file assigns a kernel module to each network device.
    For Example :- 
    [root@localhost ~]# cat /etc/modprobe.conf
    alias eth0 b44
    Here b44 is the kernel module for network device eth0.
    We can Confirm by following command (This module “b44” is present or not).
    [root@localhost ~]# lsmod |grep b44
    b44                    29005    0

    Q: - What is the location of "network" file and what does this contains?
    location :-  /etc/sysconfig/network
    This file contains following fields
    NETWORKING=yes
    NETWORKING_IPV6=no
    HOSTNAME=localhost.localdomain

    Q: - What is the role of /etc/resolv.conf file?
    In this file we sets the DNS servers (using their IP addresses) and the search domain. The values of the DNS servers are often added when the network is activated because the data can be provided by DHCP or a similar service.

    Q: - Which deamon is required to start Network services?
    network
    /etc/init.d/network start

    Q: - Which protocol is required to allow local printing and print sharing?
    Internet Printing Protocol (IPP) is required to allow local printing and print sharing.

    Q: - What is CUPS?
    CUPS stands for "Common UNIX Printing System". CUPS is a open source printing system developed by Apple Inc. CUPS uses the Internet Printing Protocol (IPP) to allow local printing and print sharing.

    Q: - What are the advantages of YUM?
    - Automatic resolution of software dependencies.
    - Multiple software locations at one time.
    - Ability to specify particular software versions or architectures.

    Q: - Which configuration file is required to change the Run Level of Server or system?
    /etc/inittab
    To change the default run level, modify this line.
    id:5:initdefault:

    Q: - In which directory RPM database stored?
    /var/lib/rpm

    Q: - How to list PCI Devices on your server or System?
    use "lspci" command.

    Q: - What is the role of "Kudzu"?
    Kudzu is used to Detect new Hardware

    Q: - What happens when you add a new device after installation?
    The Kudzu program runs each time the system boots and performs a hardware probe. If new hardware is found, Kudzu attempts to map it to a kernel module. If successful, the information is saved, and the device is configured.

    Q: - How to Enable ACLs for /home partition?
    Add following entry in /etc/fstab
    LABEL=/home    /home       ext3        acl      1  2
    Now remount /home partition with acl option.
    mount -t ext3 -o acl /dev/sda3  /home

    Q: - How to View ACLs for a file(test_file)?
    getfacl test_file

    Q: - How to remove an ACL?
    setfacl --remove-all <file-name>

    Q: - How to detect CPU architecture/bitmode (32-bit or 64-bit) for Linux ?
    # cat /proc/cpuinfo | grep flags
    you will find one of them with name "tm(transparent mode)" or 
    "rm(real mode)" or "lm(long mode)"

    1. rm tells ,it is a 16 bit processor
    2. tm tells, it is a 32 bit processor
    3. lm tells, it is a 64 bit processor

    Q: - What is the difference between LILO and GRUB ?
     1) LILO has no interactive command interface, whereas GRUB does. 
    2) LILO does not support booting from a network, whereas GRUB does. 
    3) LILO stores information regarding the location of the operating systems it can to load physically on the MBR.
    If you change your LILO config file, you have to rewrite the LILO stage one boot loader to the MBR. Compared with GRUB, this is a much more risky option since a misconfigured MBR could leave the system unbootable. With GRUB, if the configuration file is configured incorrectly, it will simply default to the GRUB command-line interface.

    Q: - What is the role of udev daemon in Unix ?
     udev is the device manager for the Linux 2.6 kernel series. Primarily, it manages device nodes in /dev. It is the successor of devfs and hotplug, which means that it handles the /dev directory and all user space actions when adding/removing devices, including firmware load.

    Q: - Can we have two apache servers having diff versions?
    Yes, you can have two different apache servers on one server, but they can't listen to the same port at the same time.Normally apache listens to port 80 which is the default HTTP port. The second apache version should listen to another port with the Listen option in httpd.conf, for example to port 81.
    For testing a new apache version before moving your sites from one version to another, this might be a good option.You just type www.example.com:81 in the browser window and you will be connected to the second apache  instance.

    Q: - How are devices represented in UNIX?
    All devices are represented by files called special files that are located in /dev directory.
    Q: - What are the process states in Unix?
    As a process executes it changes state according to its circumstances. Unix processes have the following states:
    Running : The process is either running or it is ready to run .
    Waiting : The process is waiting for an event or for a resource.
    Stopped : The process has been stopped, usually by receiving a signal.
    Zombie : The process is dead but have not been removed from the process table.

    Q: - What command is used to remove the password assigned to a group?
    gpasswd –r

    Q: - What command should you use to check the number of files and disk space used and each user's defined quotas?
    repquota 

    Q: - What is a zombie?
    Zombie is a process state when the child dies before the parent process. In this case the structural information of the process is still in the process table.

    Q: - What daemon is responsible for tracking events on your system?
    syslogd 

    Q: - If some one deletes /boot directory from your server, than what will happen?
    In that case your server will be in unbootable state. Your Server can’t boot without /boot directory because this directory contains all bootable files 

    Q: - What does /dev directory contain?
    The /dev directory contains all device files that are attached to system or virtual device files that are provided by the kernel.

    Q: - What is the role of udev daemon?
    The udev demon used to create and remove all these device nodes or files in /dev/ directory. 

    Q: - What does /etc/skell directory contains?
    The /etc/skel directory contains files and directories that are automatically copied over to a new user's home directory when such user is created by the useradd or adduser command.

    Read more...